LatestNew
In the AI era, real and fake look the same.
AI makes attacks faster and more frequent. We show you which AI is at work in your company and what it can access.
Playing loads YouTube. Privacy
SaQura helps companies protect themselves against AI attacks: we show you which AI is at work in your business, and you decide what it can access.
An AI inventory for your whole company.
We advise you on AI security and shadow AI, with no product purchase needed. The first step: a clear overview of where your company stands today.
Which AI tools and AI agents are in use, including shadow AI, and which data they can reach.
We rank the risks and show the next steps, in plain terms for management and IT.
Approval routes, the right permissions for AI agents and guidance for your team, plus quantum-safe encryption as standard protection.
Latest from SaQura
LatestNew
AI makes attacks faster and more frequent. We show you which AI is at work in your company and what it can access.
Playing loads YouTube. Privacy

The film3:44
Why post-quantum encryption matters now, and how SaQura makes it simple.
Watch the filmLatestApp Store
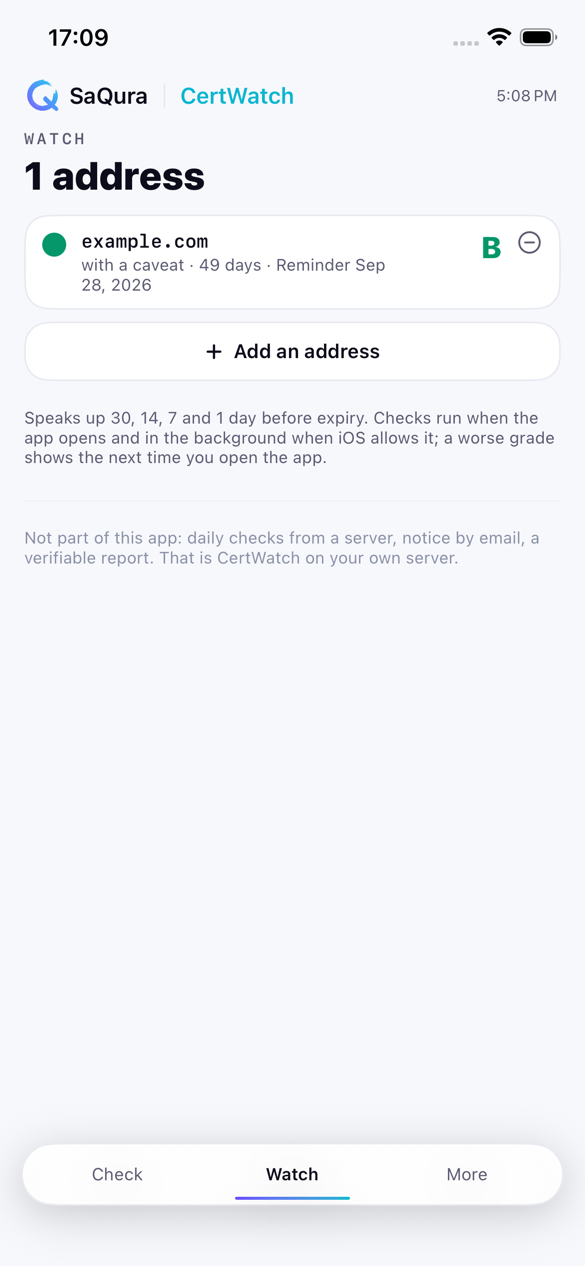
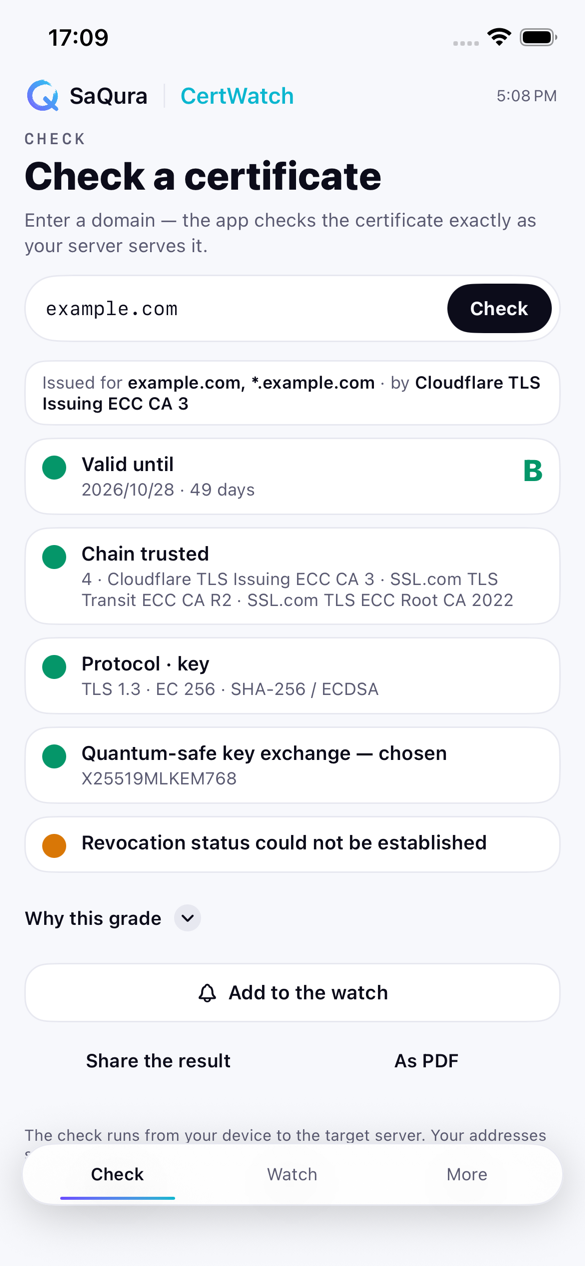
Grade A to F for any address, three addresses under watch.
1 of 3: Clip: AI security
Which AI is at work in your company, what it can access and how you secure it.
What's happening now
Shadow AI
One short prompt in a chat assistant, and quotes, contracts or customer data end up with an outside service.
AI attacks
Attackers use AI to write emails, voices and messages that feel genuine. Faster and more convincing than ever.
Excessive permissions
If an AI assistant has more permissions than its task needs, whoever takes it over can reach everything it is allowed to see.
The solution
SaQura Inventory
See which AI is running in your business and what it can access.
Learn moreConsulting and implementation
Together with you, we define which AI is allowed, remove unnecessary permissions and prepare your team for AI deception.
Learn moreSaQura Encryption
Encryption built on the new post-quantum standards: for today and for the age of quantum computers.
Learn moreOur products
Our products show which AI is running in your company and encrypt your data with quantum-safe methods.
Know what's quantum-unsafe
An app that checks your source code and server addresses and shows, in plain language, which encryption you use and what quantum computers will break, with a report and roadmap.
For: Organisations that want to document and plan their encryption for NIS2, GDPR or the BSI recommendations.
Annual license · runs locally
Encryption inside your app
Add SaQura as a package: the encryption runs entirely on your own infrastructure, your data and keys stay with you.
For: Teams who build it into their own software.
Available for:
Encryption as a service
Call a secure API. You write no encryption yourself and run no infrastructure.
For: Anyone who wants to start fast without building encryption themselves.
REST API
Encryption in your AI assistant
Give your AI assistant (e.g. Claude) secure encryption, with no coding at all. Encryption and decryption run locally on your computer; your keys and data are not sent to us or to any third party in the process.
For: Anyone using AI assistants who wants encryption without code.
Runs locally · via NuGet (dnx)
On-premise & sovereign
Run SaQura entirely on your own infrastructure, with central management, policies and MDM rollout. The server never sees plaintext.
For: Public agencies, critical infrastructure and regulated industries.
On-premise · Managed
Certificates watched, expiry reported in time
The watchdog on your own server checks your domains daily, warns you well before anything expires and documents it in sealed reports.
For: IT operations and service providers who never want an outage from a forgotten certificate again.
Annual subscription · self-host · Windows/macOS/Linux · iPhone app
Every certificate under your domain, graded
Enter your domain, pay, done: the sealed report finds all certificates for your domain recorded in the public Certificate Transparency logs, checks each address live from the outside and grades it from A to F. No installation, no credentials.
For: Management and IT who want to know today what runs under their domain and when it expires.
One-time purchase · PDF by e-mail · EN/DE/JA
CRA reporting duty since 11 September: the process, ready to use
Since 11 September 2026, manufacturers of products with digital elements report actively exploited vulnerabilities under Article 14 CRA: early warning within 24 hours, notification within 72 hours. The template turns the reporting duty into a process: deadlines, decision tree, four report texts, case log. As DOCX and PDF, in English and German.
For: Manufacturers of software and devices with software who want to know on day one who reports what, when and where.
One-time purchase · DOCX + PDF by e-mail · EN/DE
Backup only you can open
Zero-knowledge, end-to-end encrypted backup: files are encrypted on your device before they ever leave it. The storage side never sees plaintext.
For: Law/tax firms, clinics and any business with confidential, retained documents.
GDPR/GoBD-oriented · cloud or self-hosted
Password manager without an account
Passwords and notes encrypted on your own Android phone, with quantum-safe protection. No account, no cloud.
For: Anyone who wants to keep their passwords in their own hands.
Android app on Google Play
The family
Server, app, web: the same encryption, identical on every platform.
For .NET servers & desktop apps
For Android apps
For web apps in the browser
For iPhone & iPad apps
For services, scripts & data pipelines
For embedded, desktop & native code
Encryption as a hosted service
Try it from your AI assistant
Secure messaging app (E2EE)
Encrypt on one device, decrypt on any other.
One format, compatible across every platform and proven device to device. iPhone, Android, Windows, server and web share the exact same encryption. So a single solution covers your whole stack, instead of something different per platform.
The same quantum-safe encryption as the rest of SaQura, now for talking. No account, no phone number, no address book. Self-hostable and centrally managed.

Services
KyotoTech takes on the implementation, from the first review to a fully migrated system.
We find where your systems rely on RSA or ECC and move them to post-quantum methods.
Learn moreWe review applications and servers and deliver a report with clear priorities.
Learn moreWe define what your AI agents may access and keep confidential data where it belongs.
Learn moreWe build SaQura into your environment and set up operations for your team.
Learn moreNeed an app, a website or a backend? KyotoTech builds those as well. Visit KyotoTech
How to encrypt your data today against the computers of tomorrow.
And the clock is ticking: the BSI recommends an end date for relying on classical encryption alone.
BSI guidance: 2030/2031 cut-off
On 11 February 2026 the BSI recommended end dates for classical asymmetric encryption: RSA and ECC should be used on their own only until the end of 2030 for highly sensitive data, and until the end of 2031 in general. After that, only in combination with quantum-safe schemes. Public authorities and critical infrastructure are urged to migrate now.
Source: BSI TR-02102-1 (2026 edition) · BSI press release of 11 Feb 2026
SaQura brings post-quantum cryptography to .NET, Android, iOS, Web, Python and C/C++: via a package, without rebuilding your existing project. The same encryption on every platform.
Your path
You decide how much you do yourself. We take care of the rest.
SaQura Library
Your developers add SaQura via their package manager. Encryption runs on your infrastructure; your data and keys stay with you. For .NET, Android, iOS, Web, Python and C/C++.
Learn moreSaQura Crypto API
You call a secured REST API. No cryptography of your own to write, no servers of your own to run.
Learn moreConsulting and implementation
We work with you to move your systems to quantum-safe encryption. And if the right tool doesn't exist yet, we build it.
Learn moreStandards
The NIST standard, or a conservative profile with methods the BSI recommends in its Technical Guideline TR-02102-1: both are built in. One setting decides.
ML-KEM for key exchange, NIST's post-quantum standard FIPS 203.
For: teams following the international standard.
FrodoKEM-976 and FrodoKEM-1344, as recommended in BSI TR-02102-1: conservative by design and thoroughly studied for years.
For: government, critical infrastructure, anything that must stay secret for decades.
In the NIST profile we combine ML-KEM with proven classical encryption (X25519, hybrid), as the BSI recommends for the transition. If one breaks, the other holds.
In plain terms
You get the NIST standard right away. Want especially conservative methods, say for government files? Switch to the BSI profile. One setting, no rebuild.
// NIST standard: FIPS 203
var gen8 = await Quantum.GenerateKeyPairAsync(QuantumStrength.Standard, QuantumGeneration.Gen8);   // X25519 + ML-KEM

// BSI TR-02102-1, conservative
var gen6 = await Quantum.GenerateKeyPairAsync(QuantumStrength.Medium, QuantumGeneration.Gen6);   // FrodoKEM-976
Simplified example. See the docs for exact syntax.
Quantum-safe protection for those responsible, lean integration for developers, on your own infrastructure.
Proven and quantum-safe methods combined, protecting against tomorrow's computers too. For developers: implements FIPS 203, 204 and 205.
Encryption runs entirely on your side: no cloud, your data and your keys stay yours. For developers: built right into your application; only the license check may go online, and with a license file there is no outside connection at all.
Brings the cryptographic building blocks and their documentation for BSI · NIS2 · GDPR, covering the encryption part of your audit. In the Enterprise package, we build further compliance components for you on request. For developers: integrated as a package, no rewrite, identical on every platform.

Healthcare
Health data is especially sensitive and long-lived: attackers store encrypted data today in order to decrypt it later with quantum computers (“harvest now, decrypt later”). Classic encryption like RSA or ECC offers no lasting protection against that.
In healthcare this is decisive: a patient record, once leaked, cannot be taken back. The protection has to hold from the very start.
The dental clinic Hälsa Dental got ahead of it, and already encrypts patient data quantum-safe with SaQura: proven and post-quantum methods in one.
Confidentiality that lasts.
Hälsa Dental websiteHow it works
Installed as a package, integrated right into your project: your developers do it themselves.
Add SaQura to your project via the package manager, with no setup or servers of your own.
Proven or quantum-safe encryption: one setting, you decide per application.
Encrypt and decrypt your data the same way everywhere, entirely on your own infrastructure.
Available for .NET, Android, iOS, Web, Python and C/C++.
Compliance
NIS2 requires the organisations it covers to have policies for the use of cryptography, the GDPR names encryption as a safeguard in line with the state of the art, and in an audit what counts is what you can prove. SaQura supports exactly that part: built to recognised standards, with evidence for procurement and review. So you can back up the encryption part of your audit with your own team. In the Enterprise package, we build further compliance components for you on request.
Talk to usEU and national programmes fund the move to post-quantum cryptography. It's your migration project that's funded; SaQura is the tool you implement it with.
We show you which funding programmes fit your project.
Pricing
Library license and hosted API, transparently priced.
Encryption as a hosted service, cancel anytime.
Library license for your app: watermark-free, per developer.
Get a clear overview of your whole company.
Get an AI assessmentStart today and go to production with a license.
Secure it now